Overview
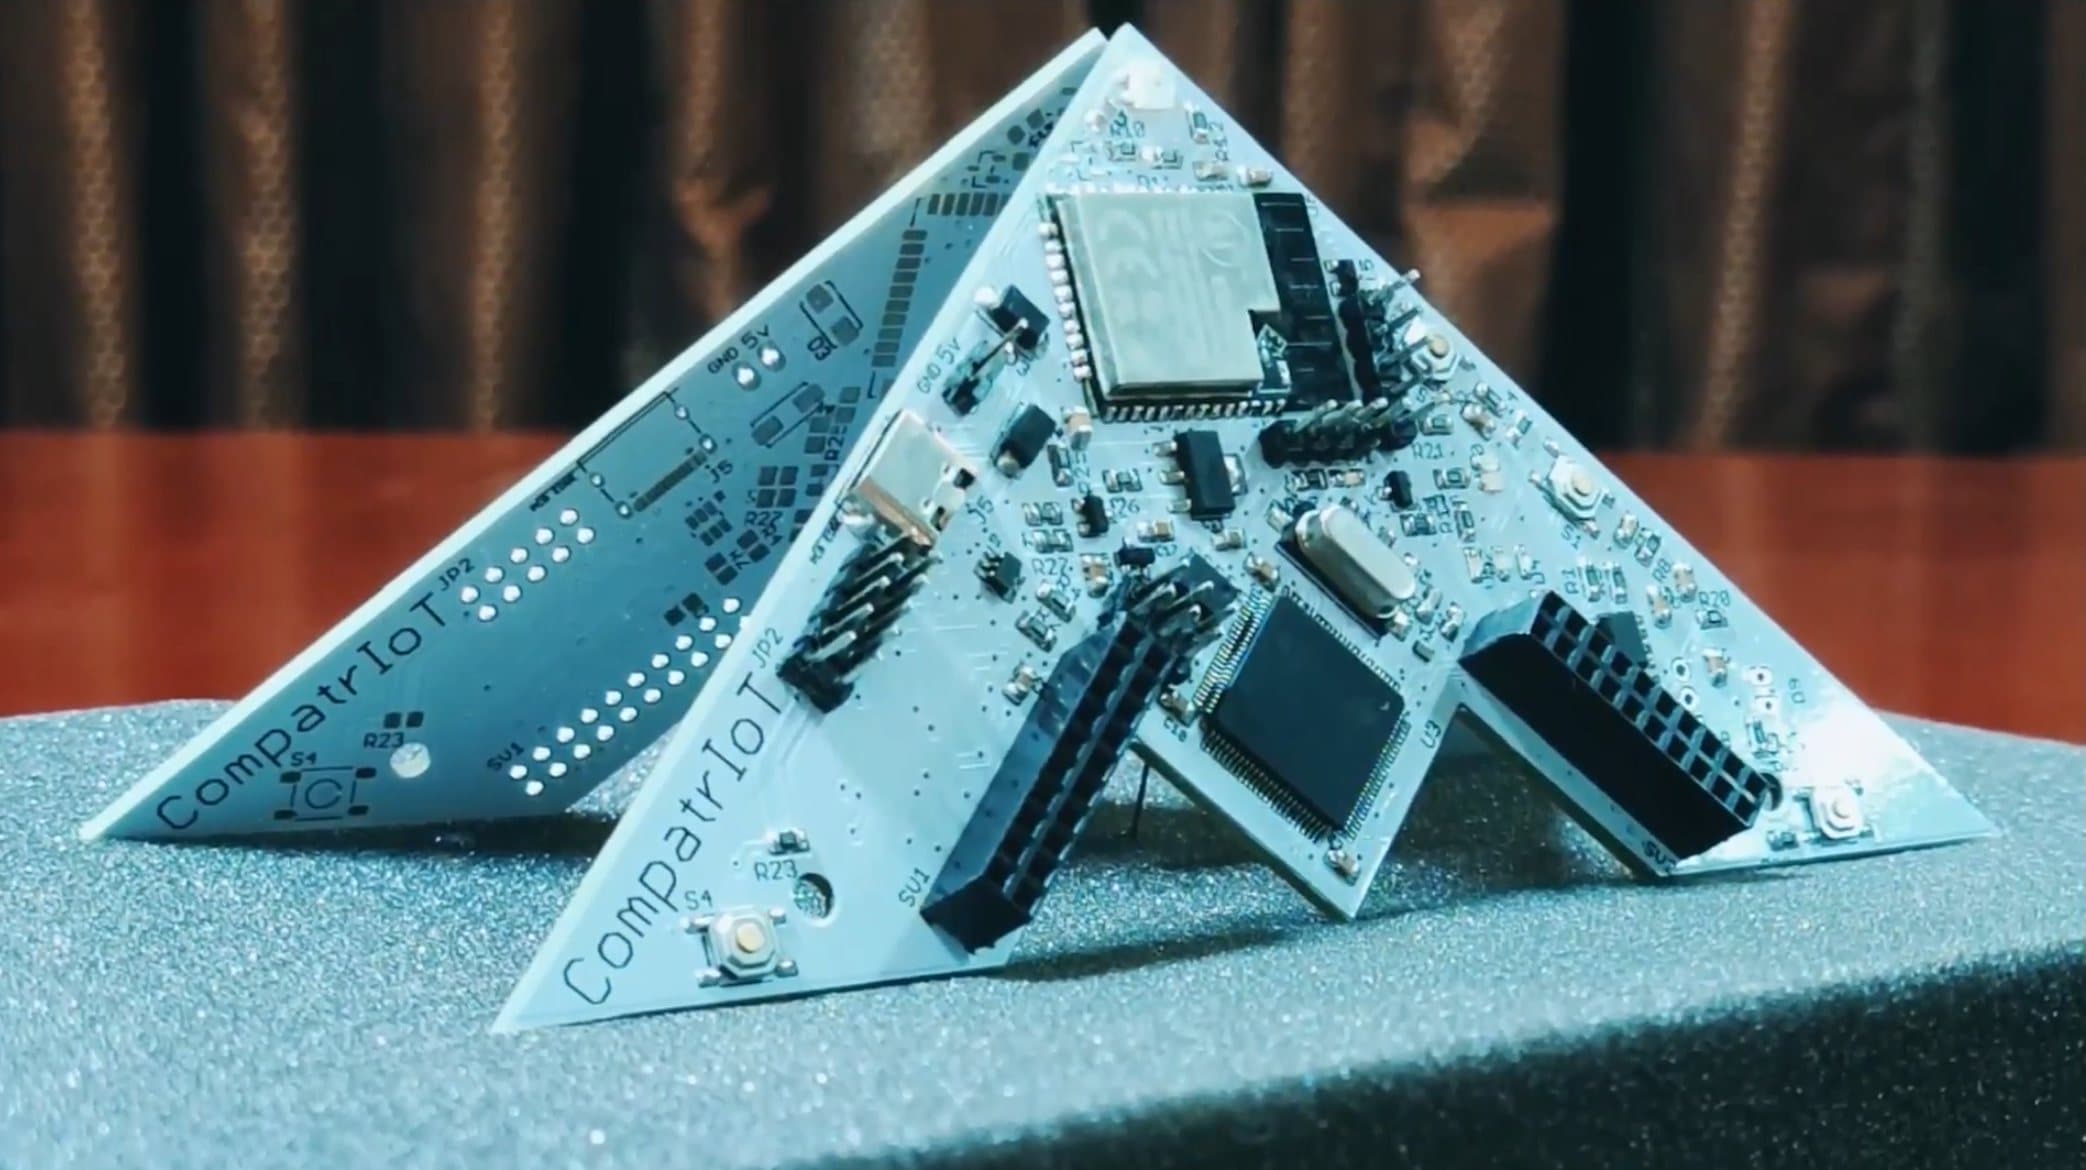
Most people learn hardware security from slides. CompatrIoT is a physical, open-source training board that you attack for real, built for security researchers, hobbyists, and students.
It compresses what usually takes a shelf of development boards and scattered CTF challenges into one board with a structured learning path.
What's on the Board
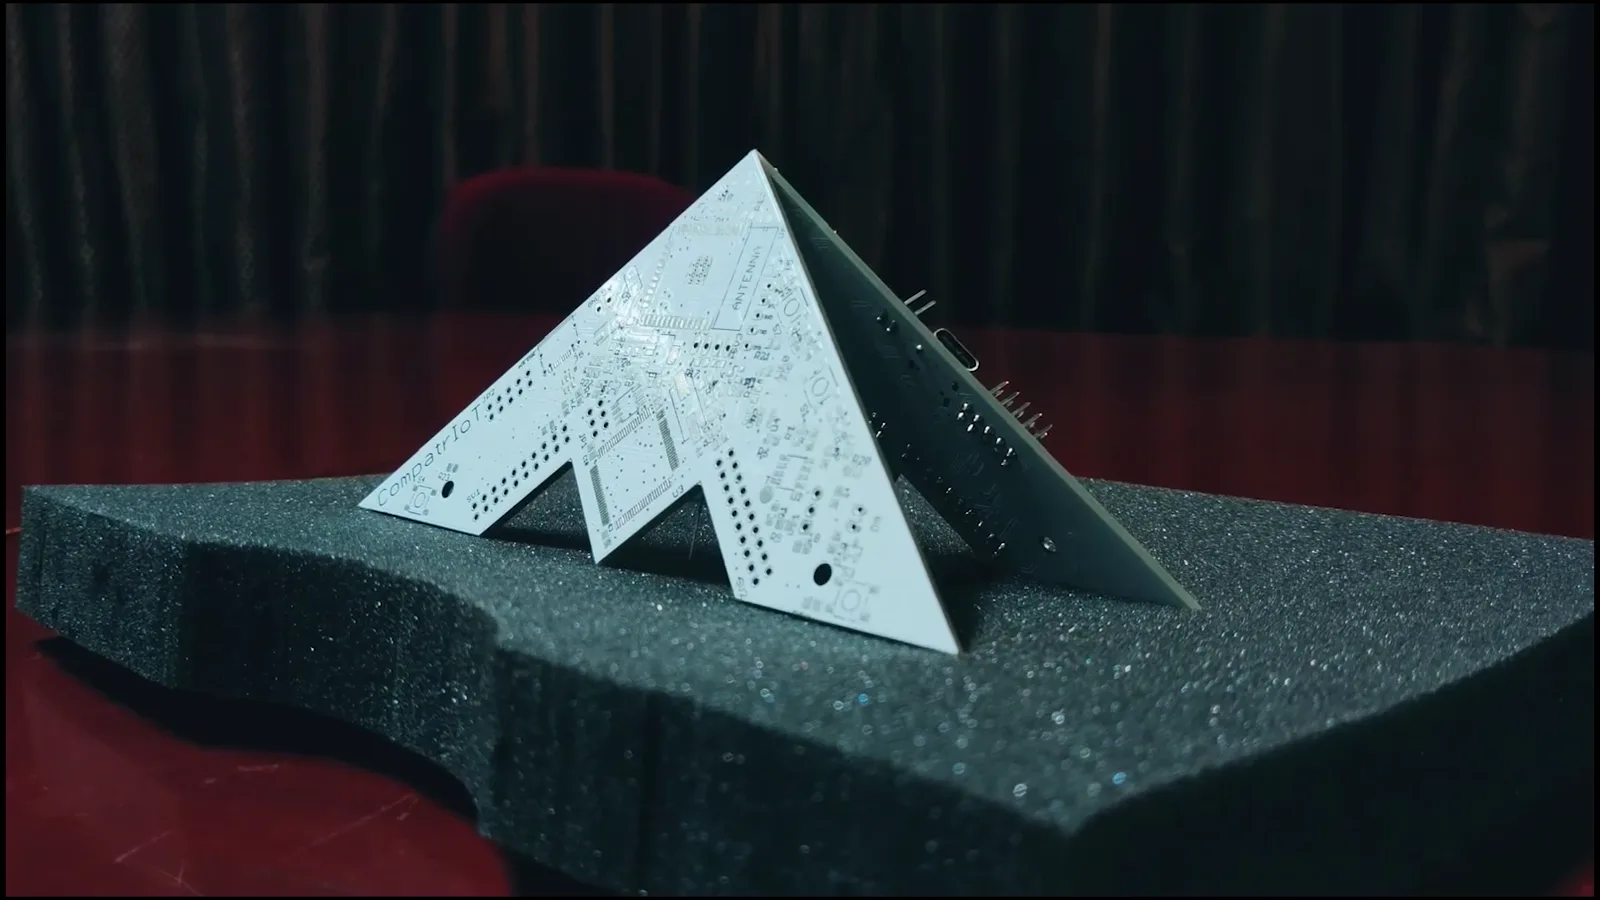
Two microcontrollers give the board broad protocol coverage, and the targets around them turn every classic hardware attack into something you can practise.
| Component | What you do with it |
|---|---|
| STM32 microcontroller | Debug ports, firmware extraction, and patching |
| ESP32 microcontroller | Bluetooth Low Energy attacks |
| SPI flash | Sniff the bus and extract firmware |
| I2C EEPROM and sensors | Reconnaissance, sniffing, and memory dumps |
| JTAG/SWD debug ports | Pinout discovery and full control of the chip |
| USB serial console | The lab console and UART exercises |
| Programmable LEDs | Visible proof that you changed the hardware's behaviour |
Twenty Labs, One Path
The labs run from first contact to full compromise, one protocol at a time, with difficulty rising as you go.

The Lab Console
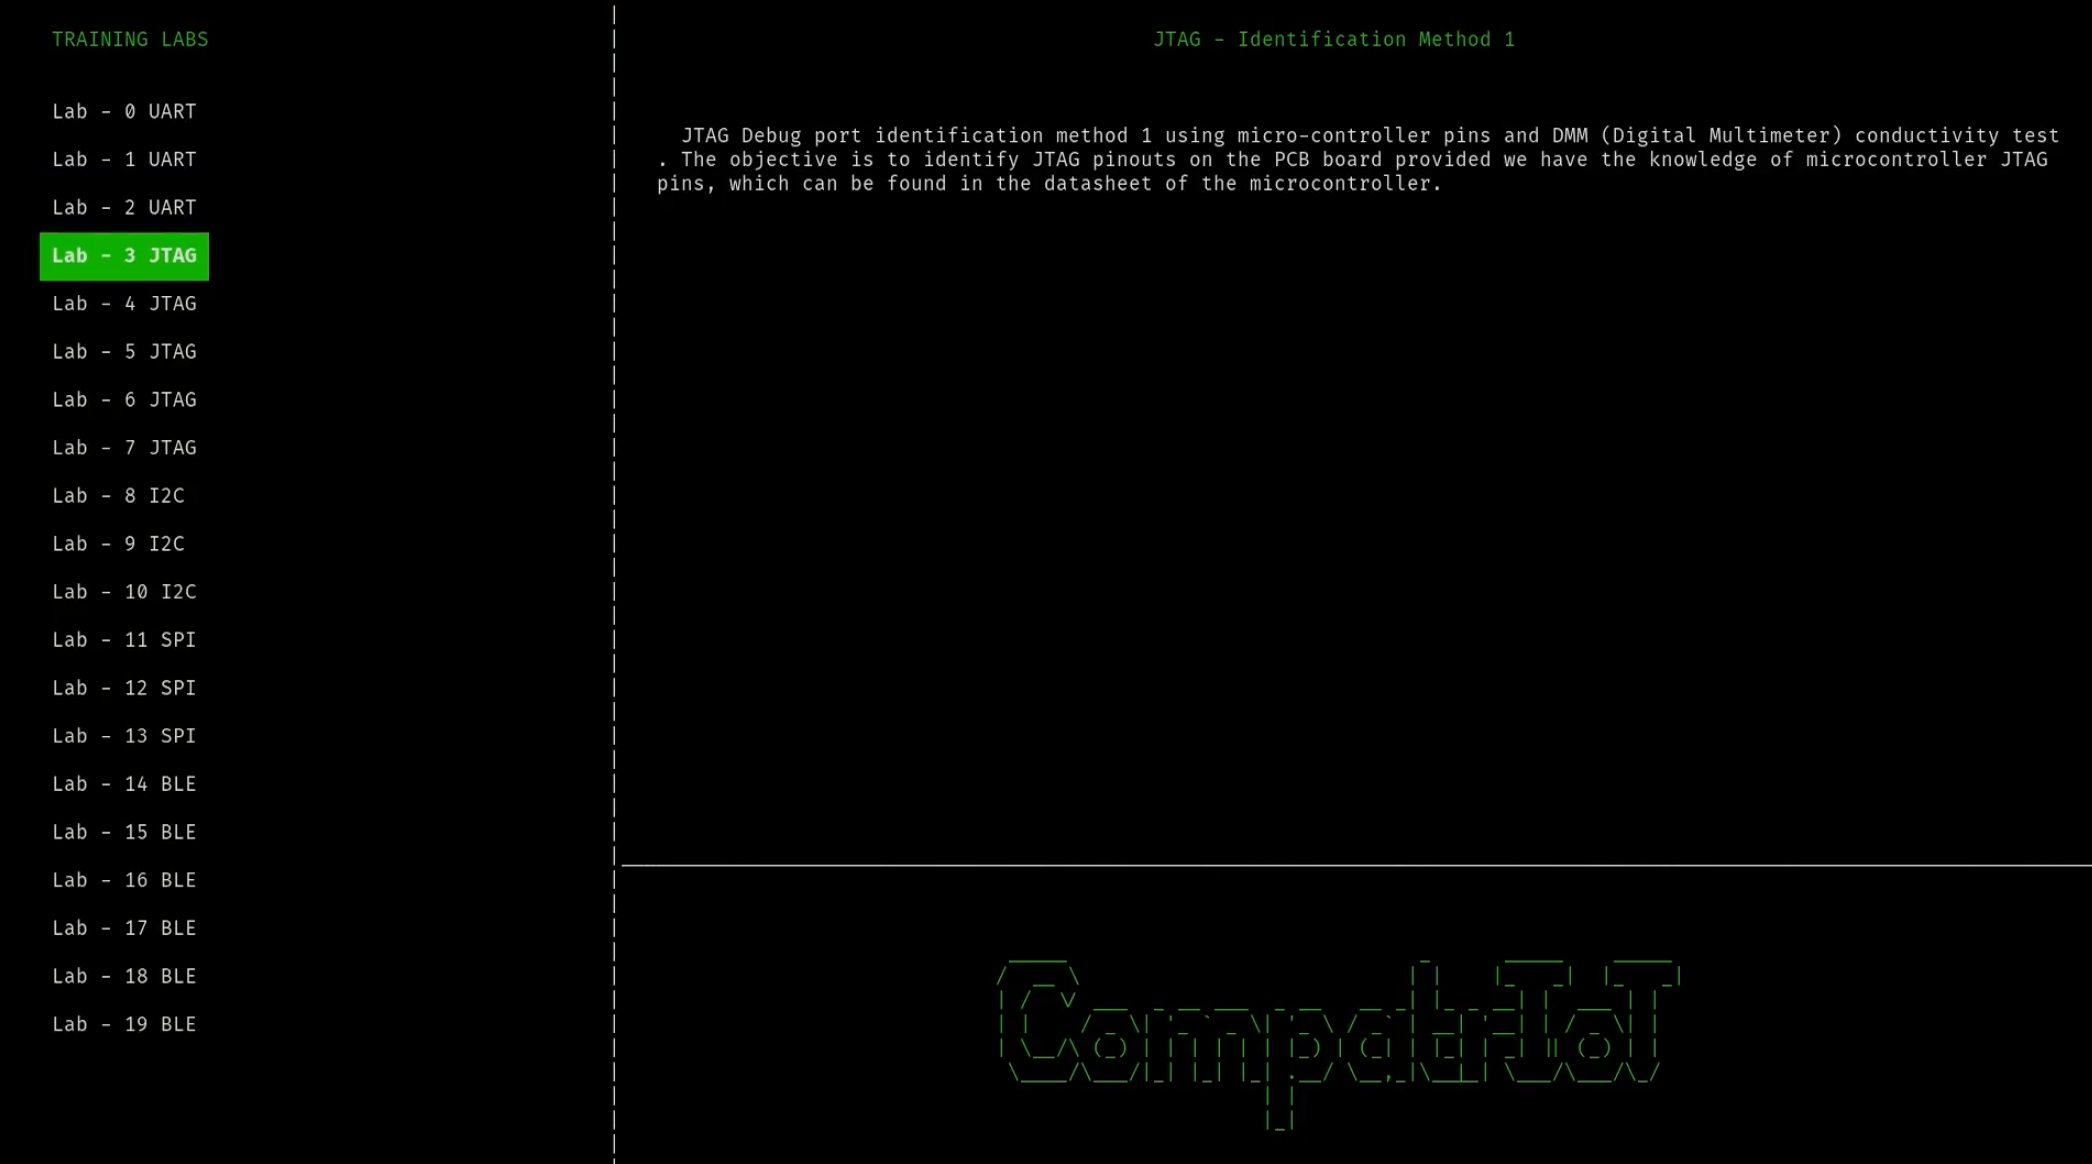
Every lab is played through a terminal-native console: the list of labs on the left, the current challenge and its objective on the right. It feels like the tools security people already use, and it keeps the focus on the hardware.
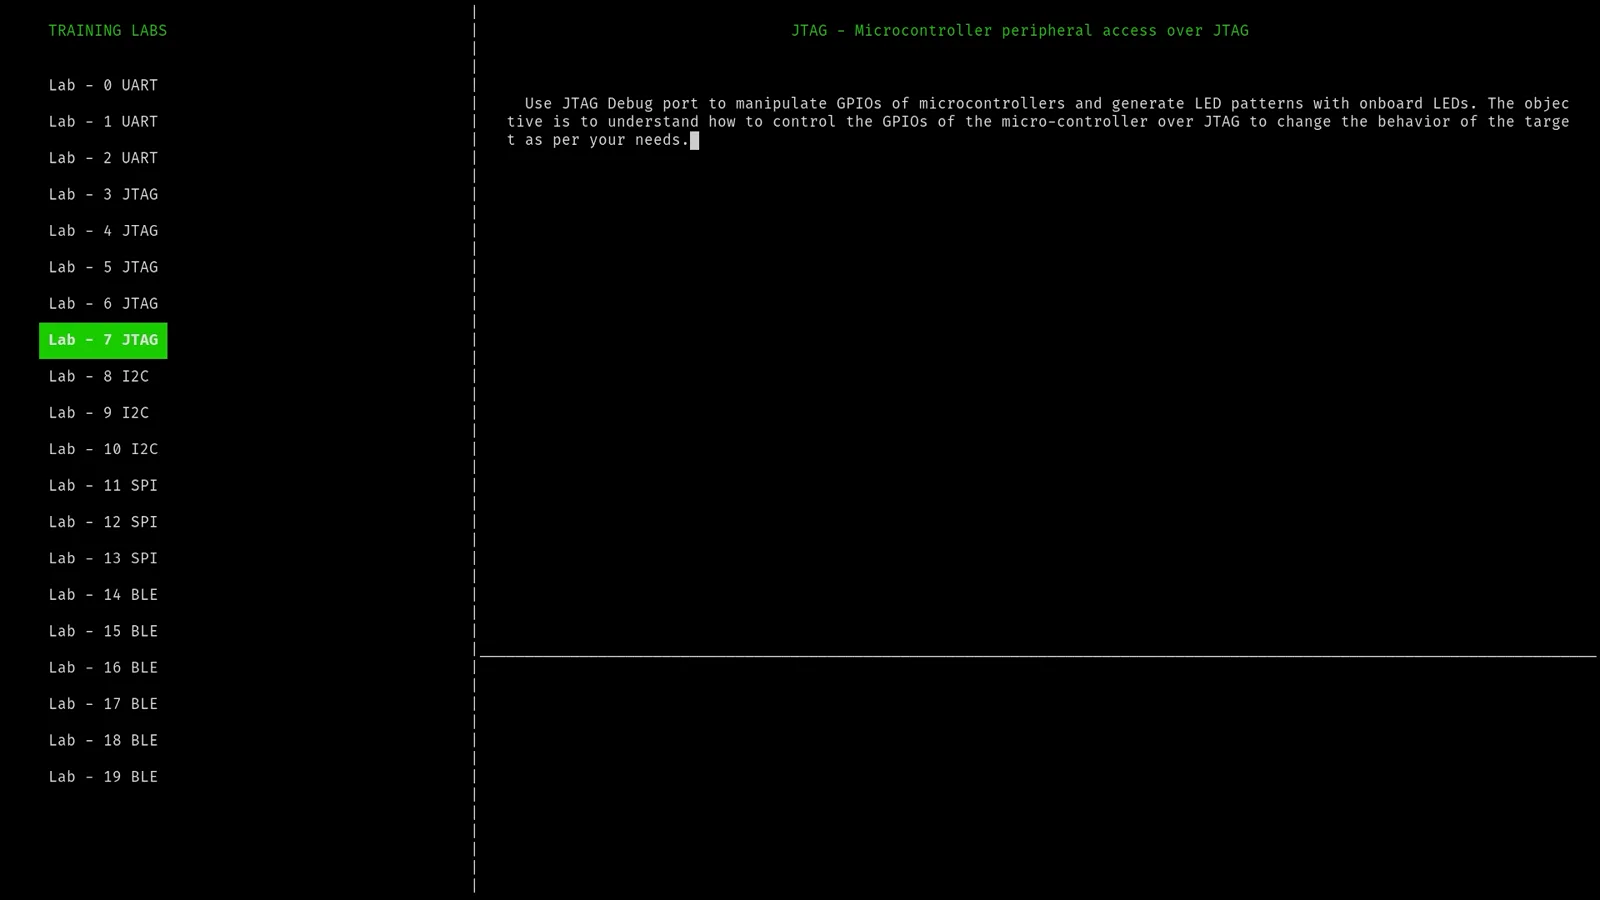
A JTAG lab, for example, asks you to use the debug port to drive the microcontroller's GPIOs and change the LED patterns: you see on the board that you've taken control.
Seeing the Signals
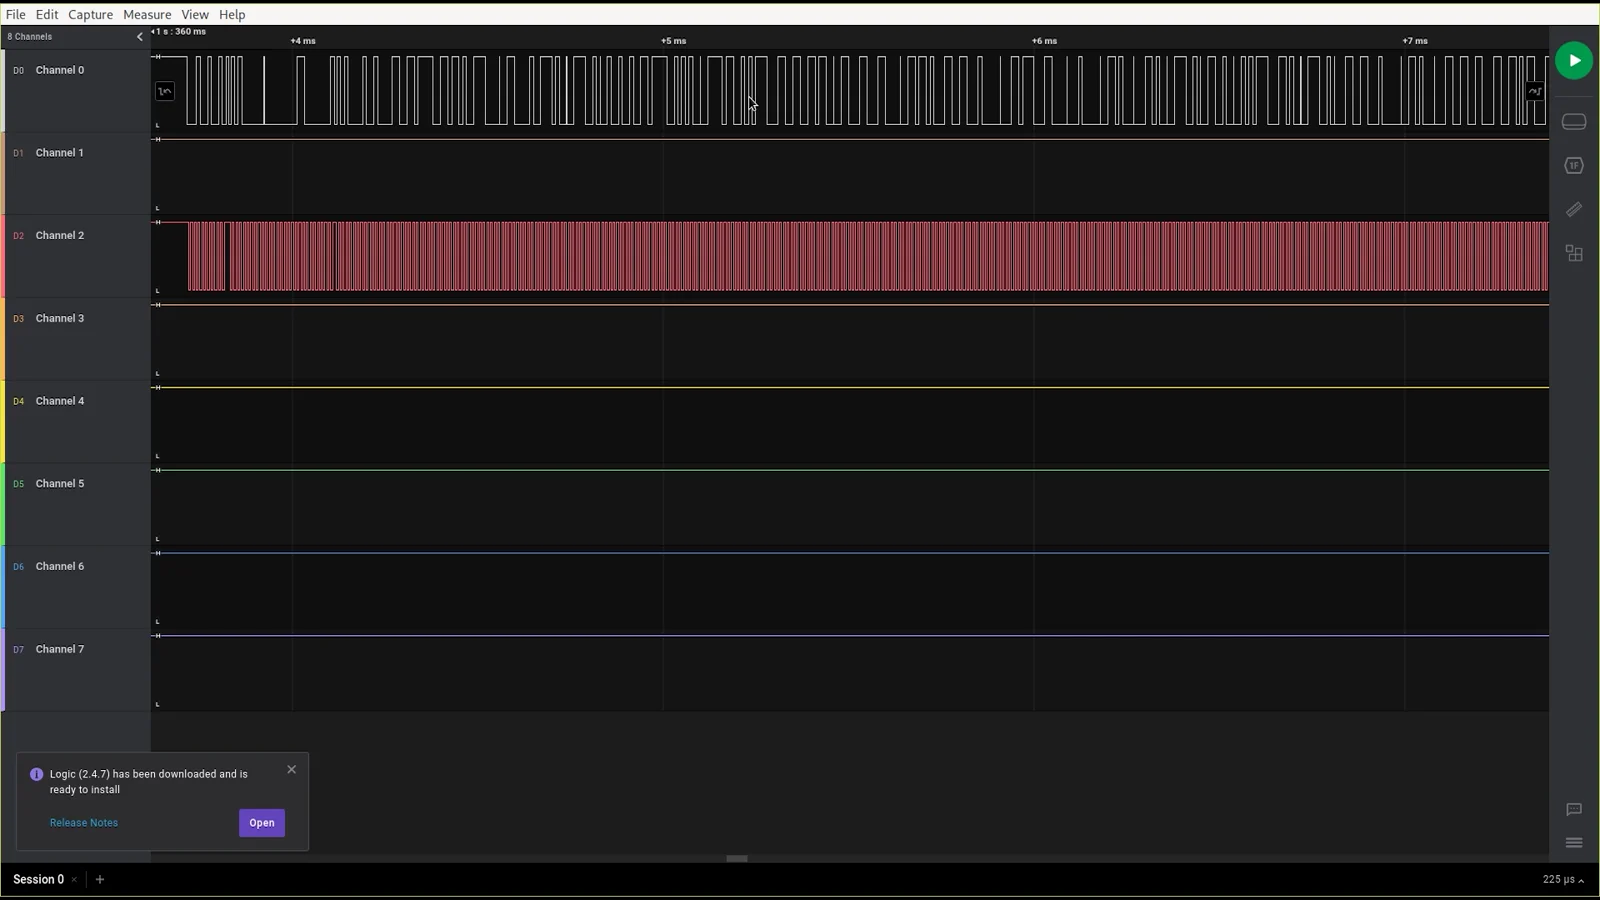
Hardware attacks are invisible until you capture them. The labs pair the board with a logic analyser, so sniffing a bus means watching real traffic, decoding it, and pulling secrets out of it.
| Skill | How the labs teach it |
|---|---|
| Finding interfaces | Identify ports and pinouts on real hardware |
| Sniffing | Capture I2C, SPI, and BLE traffic and decode it |
| Extraction | Dump memory and firmware from real chips |
| Exploitation | Patch firmware, take over GPIOs, crack a BLE key |
Why It's Open
The hardware designs, firmware, and documentation are all open, so anyone can build the board, extend the labs, or teach with it.
| Without CompatrIoT | With CompatrIoT |
|---|---|
| A shelf of different dev boards | One board |
| Scattered CTF challenges | Twenty labs in order |
| Slides about attacks | Attacks on real hardware |
| Closed training kits | Open designs anyone can build |